HIPAA Compliance Statement
Dayyani Solutions LLC engineers the ViacoraMed Autonomous Medical Coding and Clinical Documentation Integrity (CDI) platform from the ground up to exceed the statutory requirements of the Health Insurance Portability and Accountability Act of 1996 (HIPAA), the HITECH Act, and 45 CFR Parts 160 and 164.
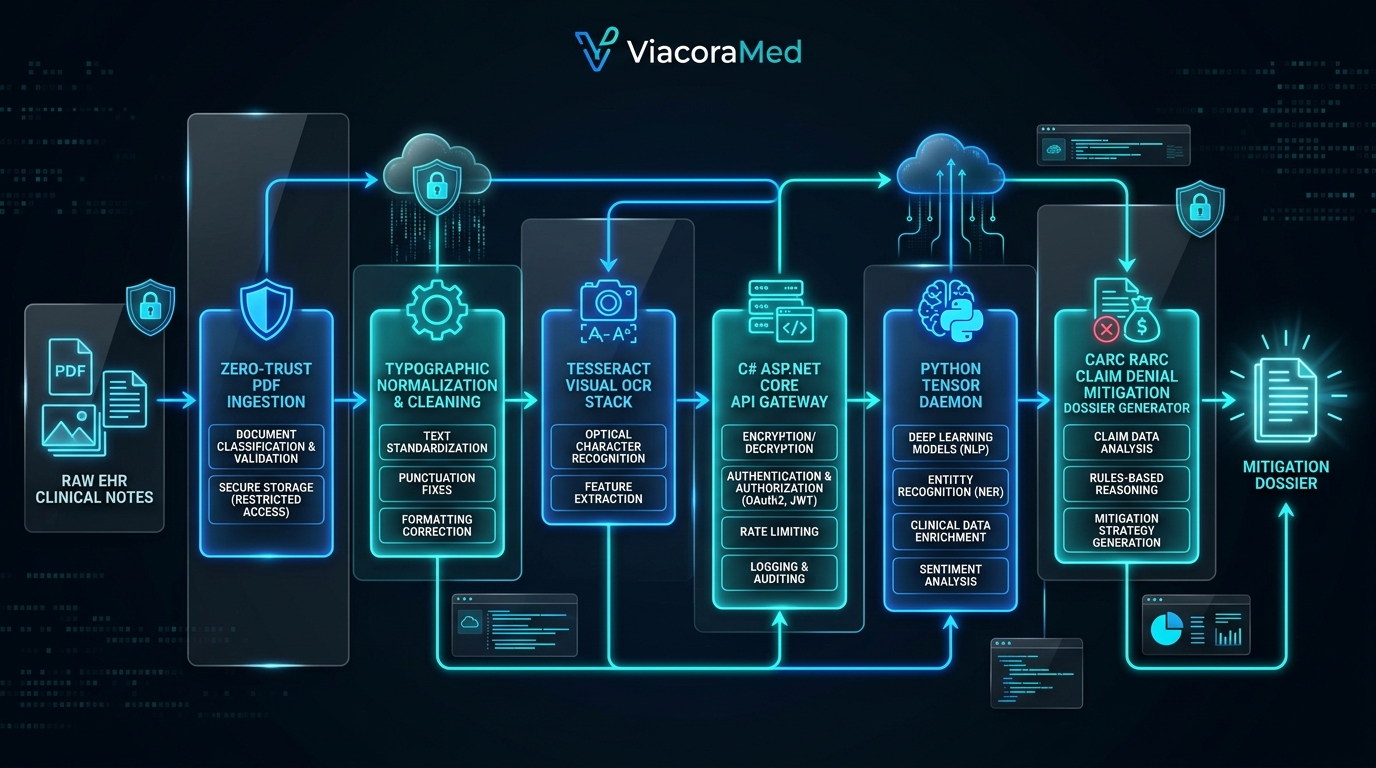
Zero-Trust In-Memory RAM Anonymization Before AI Specialist Inference
Every patient chart uploaded via PDF/OCR or streamed via Direct EHR Integration (`HL7 FHIR R4`, `HL7 v2.5`, `C-CDA`) passes through ViacoraMed's deterministic Safe Harbor RAM Scrubbing Gate prior to multi-agent consensus routing. All 18 statutory HIPAA identifiers (names, MRNs, SSNs, dates, addresses, contact numbers, account/plan numbers, and device identifiers) are scrubbed in volatile memory, ensuring 0% PHI leakage to external model endpoints.
Administrative, Physical & Cryptographic Technical Controls
Strict role-based access control (`Doctor`, `NP`, `Medical Coder`, `HIM Administrator`), cryptographic JWT session enforcement, automatic session expiration, and two-factor OTP authentication.
Every chart ingestion, stage execution (`processed_cases.stage_logs`), and clinical code remediation is permanently recorded in PostgreSQL (`case_audit_logs` & `security_audit_logs`) with actor identity and UTC timestamps.
Outbound 837P claims, clinical remediation directives, and executed HIPAA BAAs are protected against improper alteration using SHA-256 cryptographic tamper digests.
All clinical payloads and API transactions enforce TLS 1.3 with HSTS in transit and AES-256-GCM encryption at rest across tenant-isolated PostgreSQL storage.
Online ESIGN Act (15 U.S.C. § 7001) BAA Execution & Statutory Signatory Authority
ViacoraMed provides covered healthcare entities with turnkey online Master HIPAA Business Associate Agreement execution via our cryptographic BAA vault (/sign-baa), capturing drawn HTML5 canvas signatures, IP/UTC forensic metadata, SHA-256 tamper digests, and downloadable counter-signed PDFs: